Add as preferred on Google

A Comparative Study of RAG and GraphRAG Using DatabricksRead More
A vibe-coded prototype suits idea validation, but any feature touching revenue, compliance or customer trust needs a hardening pass before release.
Audit the prototype against the hardening steps before the next release or customer commitment.
A working AI-built prototype leaves CTOs and founders with one decision: ship it, harden it or rewrite it. The answer affects stability, security, scalability and the cost of fixing problems after launch. In our experience, fixing it after launch usually costs more than building it right first.
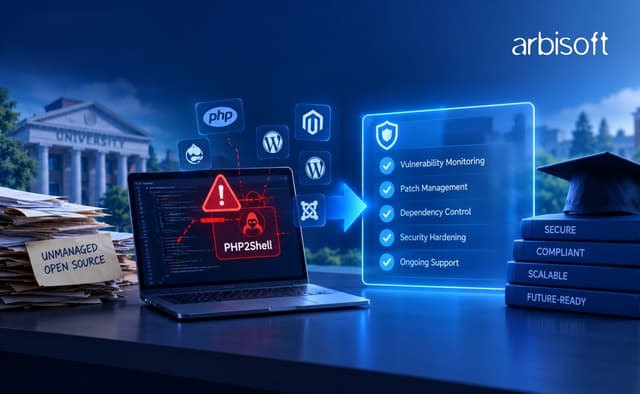
A vibe-coded prototype is for validating an idea. Anything that touches revenue, compliance or customer trust needs a hardening pass before release. This article covers what production-ready means, the main risks, the transition steps and a decision rule for when to harden.
Shipping prototype code turns a technical shortcut into a business risk once real customers, uptime or compliance depend on it.
Startups and scale-ups operate under constant pressure to release features quickly. Investors want rapid growth and visible progress. Customers expect smooth performance from day one. Balancing those demands means deciding early when to prioritise speed and when to prioritise resilience.
If uptime, compliance, or customer trust is at stake, shipping vibe-coded prototypes can jeopardise future releases and your market reputation.
Investors care about scalability and predictable returns. They expect products to perform under real-world loads without unexpected downtime. A product that fails under customer demand creates revenue risk and erodes confidence.
A vibe-coded prototype can secure a funding round if it demonstrates potential. But without production coding practices, that same code will likely require costly rewrites before it can serve paying customers.
A fast release helps with market entry but can hinder scaling if the code is not architected for growth. Quick, patch-based builds often lack modularity, making it difficult to integrate new features or expand into new regions without extensive rework.
Production-ready code is designed with scalability in mind. This means database schemas that can handle higher volumes, APIs that can support new integrations, and infrastructure that can be scaled horizontally without performance degradation.
Production-ready code is functional, stable, maintainable, secure and performance-tested. It includes documentation, automated tests, and version control practices that allow other developers to work on it without guesswork.
It can be deployed with confidence, knowing that the risk of critical failures after release is minimal.
Production coding is:
These characteristics allow teams to ship updates without introducing new instability.
SOC 2 is not a regulation. According to the AICPA, SOC 2 is part of its System and Organization Controls (SOC) suite of services that CPAs provide, and a SOC 2 report covers an examination of controls at a service organization. The specific obligations for a product should be confirmed with a qualified compliance or legal adviser.
Meeting these requirements means securing data storage, managing access controls, and logging activity for audits. Performance testing under realistic workloads matters just as much. If your service is expected to handle heavy traffic, testing at only a fraction of that load will give you misleading results.
The OpenSSF glossary defines vibe coding as generating and accepting AI-generated code without reviewing or understanding it. In practice, teams use the term more loosely for fast, prompt-driven builds that put speed and iteration ahead of stability. Vibe coding is useful in early product discovery, but it lacks the safeguards that production environments need.
A vibe-coded prototype is an early-stage build that demonstrates features without meeting production standards. It may rely on third-party templates, generated code, or simplified integrations.
It is useful for validating ideas and gathering early user feedback. However, without a transition plan, these prototypes become liabilities when moved to live environments.
Vibe coding is one way of doing AI coding, so the two overlap. AI coding covers any use of tools that generate or assist with writing code. Vibe coding means accepting AI-generated output without reviewing or understanding it. AI coding can produce production-ready code when engineers review, test and own the output. Vibe coding skips that review and puts speed ahead of completeness.
Manual coding is deliberate and methodical. It involves architectural planning, technical specifications, and careful implementation. Vibe coding skips these stages to produce something functional in the shortest time possible.
Manual coding is slower but produces maintainable, production-ready code. Vibe coding works for proofs-of-concept or demos but requires significant rework for production deployment.
The choice between a vibe coding MVP and a production-ready product depends on business goals, risk tolerance, and target audience.
A prototype is a concept model, often non-functional or partially functional. An MVP is a minimal product that works in real-world conditions and collects data for further development.
The difference between MVP and prototype lies in purpose: a prototype tests possibilities, while an MVP validates a market hypothesis.
A healthy product lifecycle moves from prototype to MVP, then to production deployment. Each stage requires a higher standard of code quality, testing, and documentation.
Skipping the hardening phase between MVP and production results in unstable systems and technical debt. At Arbisoft, we bridge the gap from a vibe-coded prototype to a fully production-ready product, helping you complete your build and launch with confidence.
The main risks are poor performance under load, inability to scale, and unresolved security gaps. Prototypes are built to show an idea quickly, so they rarely include the safeguards that keep a live system stable.
Problems usually show up first in the database, during traffic spikes and at access boundaries. Vibe-coded systems often lack:
Typical failures include:
Without these safeguards, performance and security problems will grow as usage grows.
Technical debt from vibe coding includes duplicated logic, inconsistent naming, and weak error handling. This debt increases the time and cost of future changes, making teams slower to respond to market demands.
We have explored these risks in detail in our blog on vibe-coding challenges, including debugging complexity, hidden technical debt, and AI-driven security gaps.
Our view is that vibe coding changes how developers work more than whether teams need them. In our experience, AI-assisted development speeds up routine tasks such as scaffolding and boilerplate, but architecture decisions, code review and compliance sign-off still need experienced engineers.
AI tools can generate code and flag common issues, but the team is still accountable for whether that code meets its compliance obligations and fits the long-term architecture. Automation handles pattern recognition well. The output still needs review by engineers who know the product's regulatory context and growth plans.
Vibe debugging, fixing problems on the fly, might solve an immediate issue, but it rarely addresses root causes. Production debugging uses logs, monitoring tools, and structured testing to resolve issues permanently.
Transforming a prototype into production-ready code involves a systematic review, refactoring, and strengthening of every critical component.
These steps reduce the chance that growth exposes problems the prototype never had to handle.
Lead architects set coding and architecture standards. Product teams ensure features are prioritised without sacrificing stability. Clear ownership prevents last-minute compromises that lead to instability.
The right level of code quality depends on the feature's strategic importance, user expectations and the cost of failure. Use prototypes for concept validation. Use MVPs for market testing. Use production code for features that impact revenue or customer trust.
If compliance, uptime, or customer retention is involved, invest in production readiness before release.
The code audit also settles whether to harden or rebuild. Hardening the existing code makes sense when the core data model and architecture hold up. A rebuild of the affected parts is the better plan when the audit shows the data model, authentication or core architecture would need to be replaced anyway.
Vibe coding is a fast way to validate ideas, and it has a place in discovery work. Any path that touches revenue, compliance or customer trust should be treated as production code from the moment real users depend on it. AI-generated code can ship to production once engineers have reviewed, tested and hardened it. The risk sits in code that nobody has checked, whatever tool produced it.
Before the next release or customer commitment, audit the prototype against the hardening steps above. Check dependencies and secrets, confirm authentication on every endpoint, add the CI gate and monitoring, and load-test at the traffic you expect. The audit results then show whether to harden the current build or rebuild the parts that will not hold.
If your team is working with a vibe-coded prototype but needs the stability, scalability, and compliance of production-ready code, our engineers can help you take it to production.
At Arbisoft, we specialize in turning early prototypes into market-ready MVPs. We help teams that started in Replit, Lovable.dev or a similar tool move their build to production.
We can run a full code audit, build a scalability plan or harden security and compliance before launch.
Contact us today to discuss your project and get expert guidance on taking your build from functional to production-ready.
It depends on the size of the codebase, how much test coverage already exists and the compliance scope the product has to meet. A small app with a clean data model may need light hardening. A regulated product usually needs more work. A code audit is the reliable way to estimate the effort before committing to a launch date.
Harden it when the data model and architecture hold up under review, because most fixes can then be made in place. Rebuild only the parts where authentication, the data model or the core architecture has to change. A code audit shows which parts belong in each group.
Yes, once engineers have reviewed it, tested it and taken ownership of it. AI-generated code that passes the same reviews, tests and security checks as hand-written code can ship. The risk comes from code accepted without review, because nobody on the team knows how it behaves under load or where its security gaps are.
That depends on what your customers ask for, because SOC 2 is a report on an examination of controls at a service organization, not a law. A qualified compliance adviser should confirm which requirements apply to the product.
...Loading Related Blogs
Trusted by top platforms for our transformative solutions and exceptional results: